Truth. Protection. Action.
“We don't just respond to digital threats — we anticipate them. Digital forensic specialists, cybersecurity experts, and corporate investigators dedicated to keeping you safe.
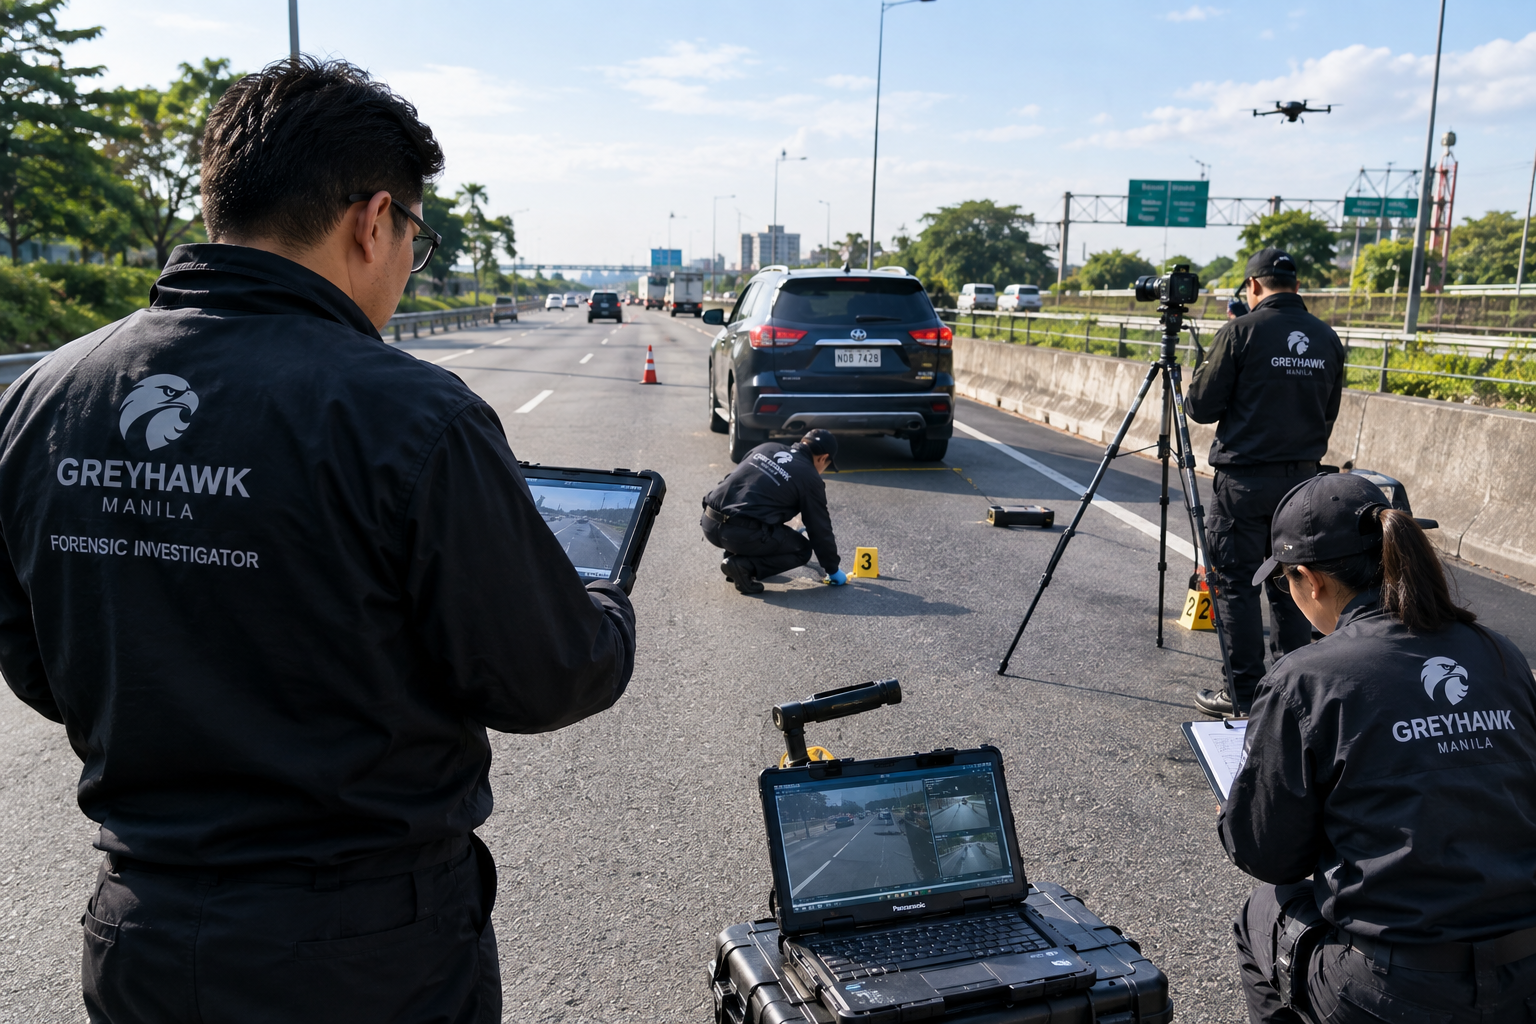
Greyhawk Forensics Manila is the Philippines' premier AI-powered digital forensics and cybersecurity firm. We combine active forensic casework, proprietary AI platforms, and a global training academy to deliver investigative solutions that are technically unmatched and legally defensible.
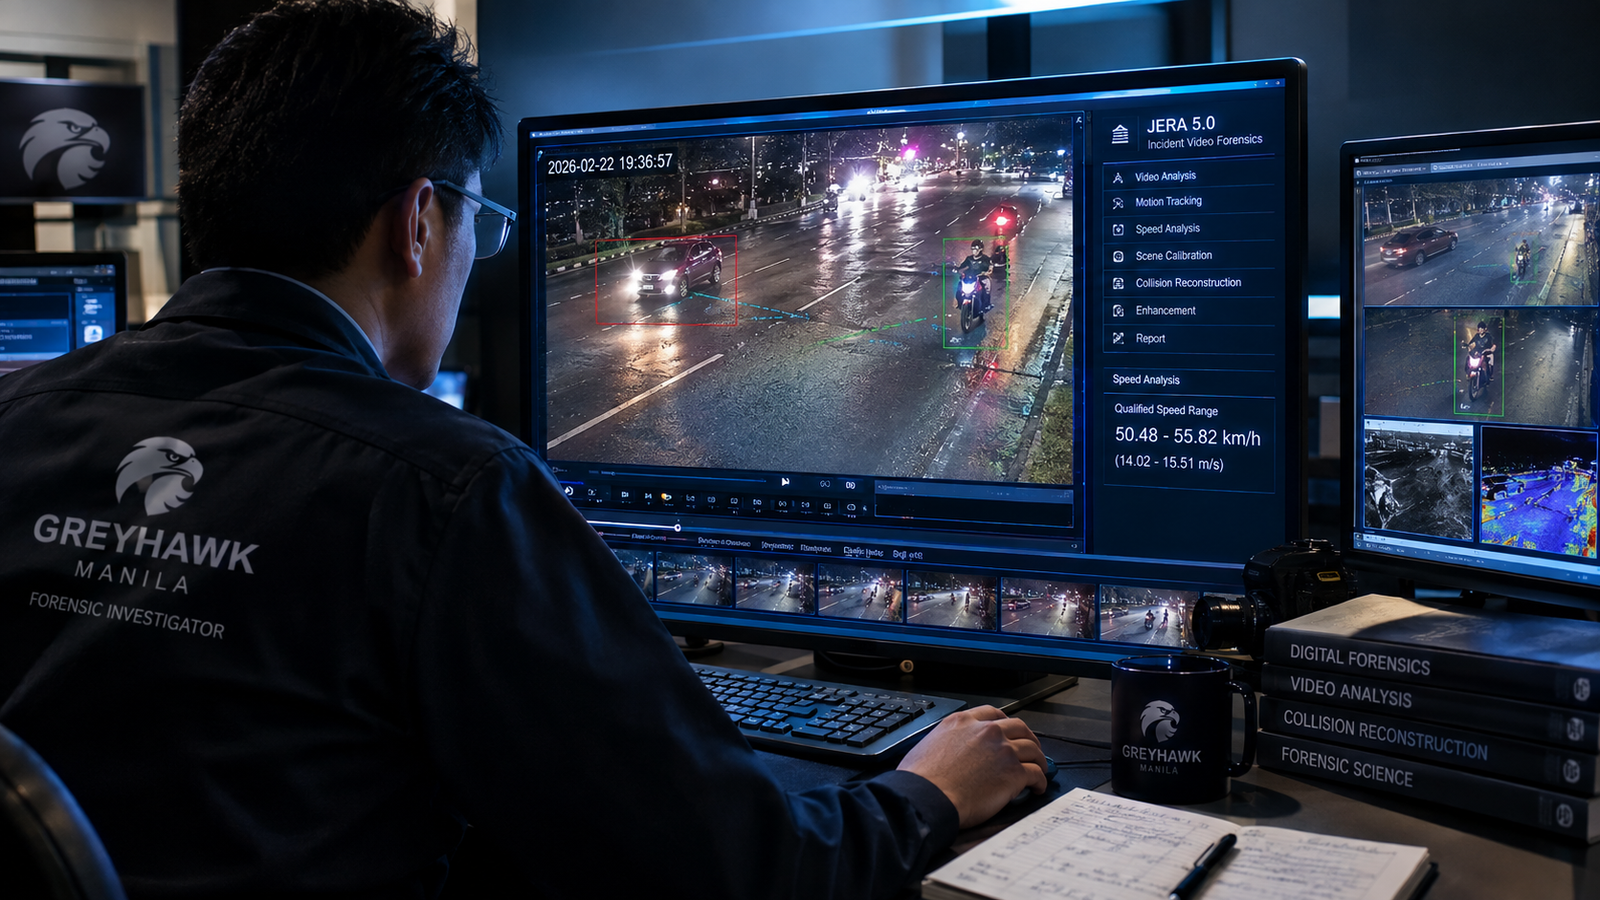
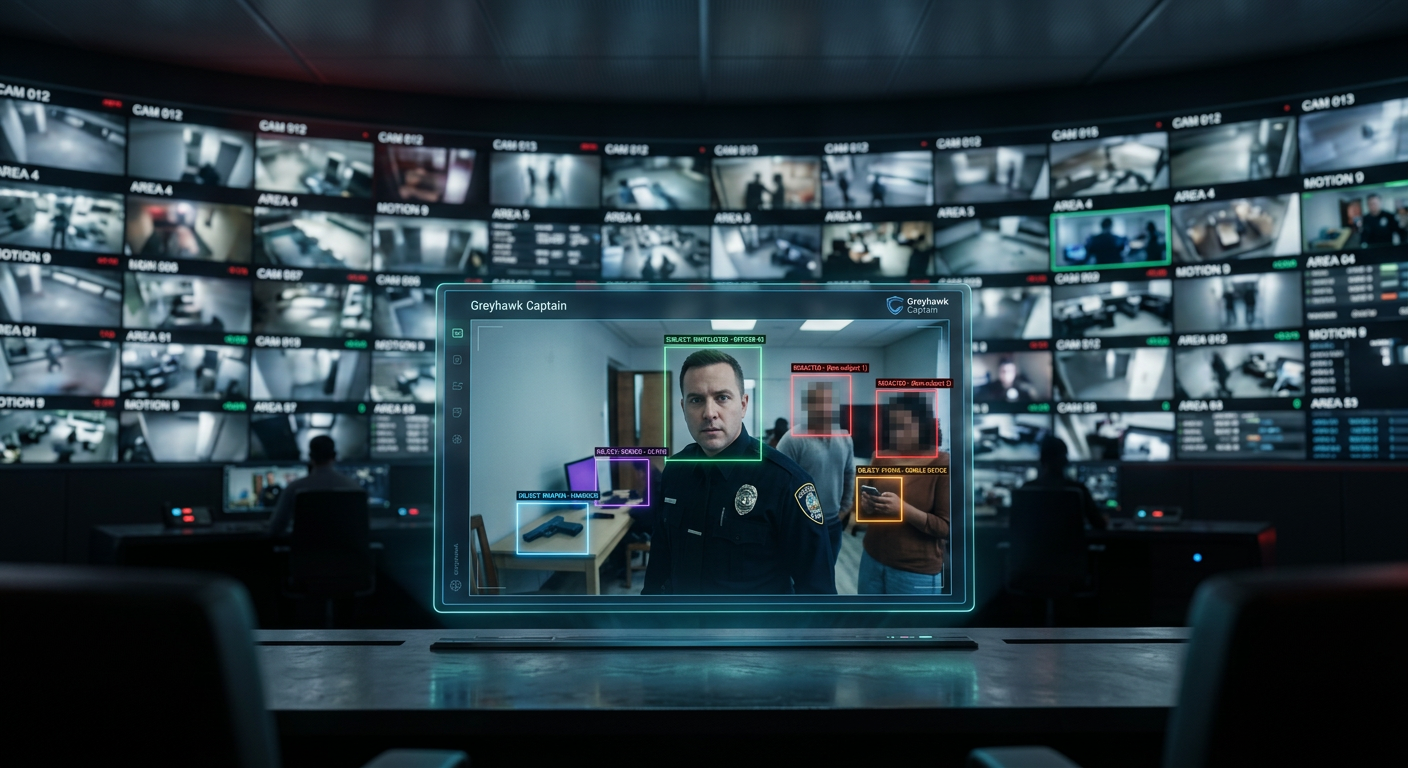
Tomorrow's technology for today's investigations. We harness artificial intelligence to uncover hidden patterns, predict threats, and decode complex digital evidence faster than ever before.
Greyhawk's proprietary suite of AI-powered platforms working together to deliver comprehensive forensic intelligence
A structured, court-ready methodology from initial report to final delivery — transparent at every step.
Submit your incident via our secure client portal, hotline, or in-person intake. We treat every report with strict confidentiality.
Our forensic analysts evaluate scope, severity, and required resources to build a tailored investigation plan.
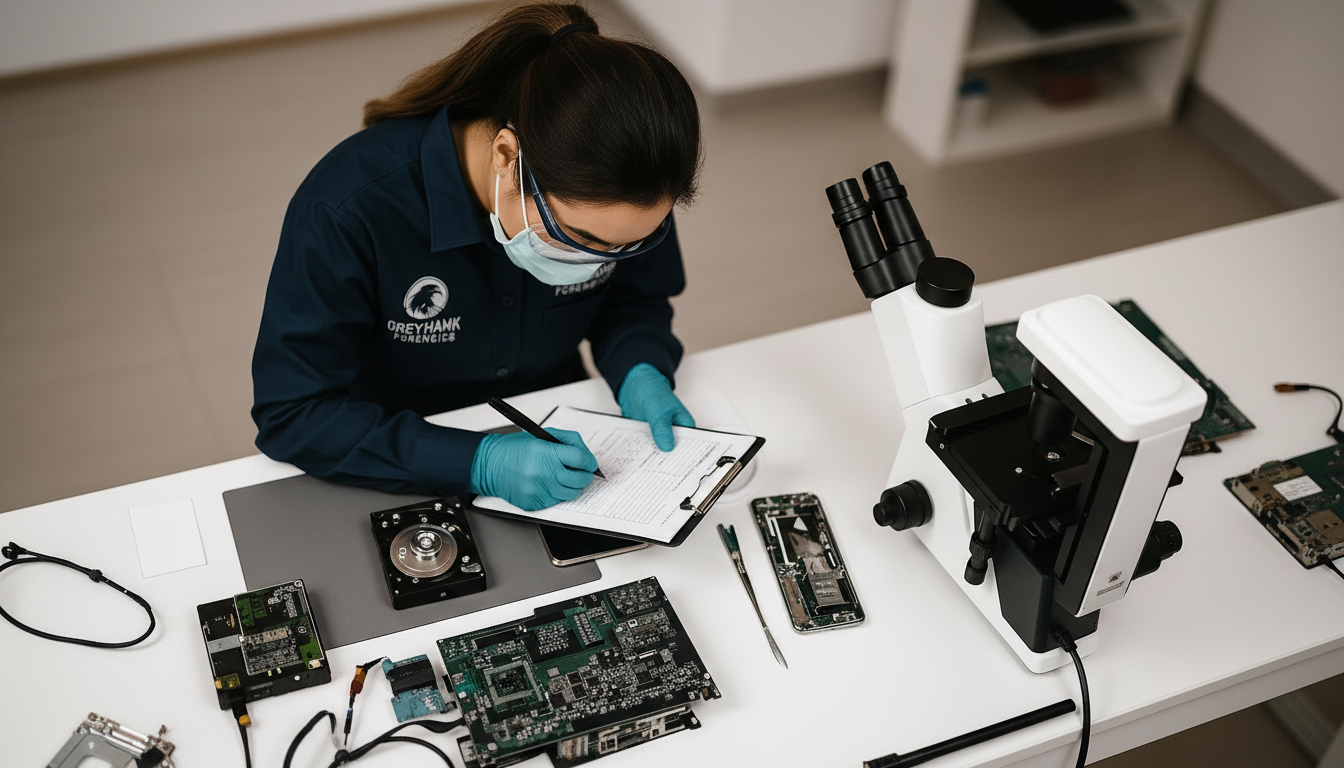
Deep-dive forensic analysis using AI-powered tools, proven methodology, and strict chain-of-custody protocols.
Court-ready reports, evidence preservation, and optional expert witness support — all fully documented.
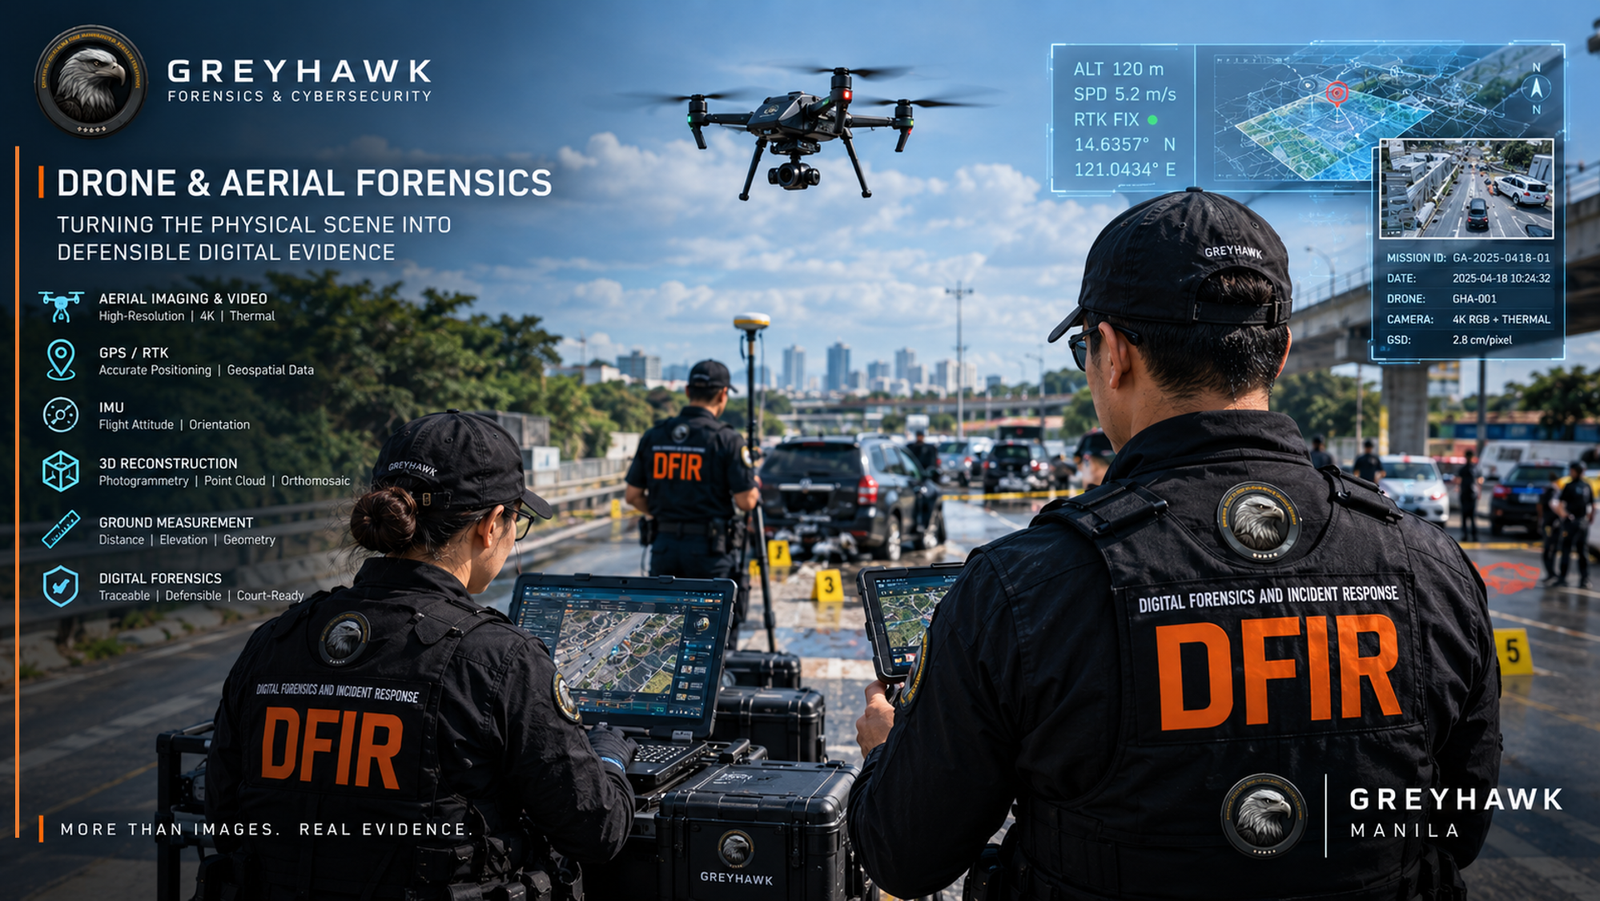
Greyhawk Manila provides digital forensics, incident response, cybersecurity, corporate investigations, video and multimedia forensics, reverse engineering, malware analysis, threat intelligence, data-privacy forensics, AI-assisted forensic analysis, IoT and smart-device forensics, and specialized technical investigations. Services are tailored to the nature of the incident, available evidence, client requirements, and authorized scope of work.
Digital forensics focuses on examining digital evidence to determine what happened, how systems or accounts were affected, what artifacts remain, and what conclusions can be supported by the evidence.
Cybersecurity focuses on preventing, detecting, containing, and responding to security threats.
Greyhawk combines both capabilities where appropriate, allowing an incident to move from detection → response → evidence preservation → forensic investigation → remediation → security validation.
Yes. Greyhawk can support authorized incident response and digital forensic investigations involving compromised servers, websites, endpoints, accounts, cloud environments, databases, malware, ransomware, unauthorized access, suspected data exposure, and other cyber incidents.
The exact response depends on the affected environment and the evidence available.
Greyhawk can investigate potential initial-access mechanisms by correlating available evidence such as authentication records, server logs, application logs, endpoint artifacts, network telemetry, vulnerabilities, malware, webshells, cloud activity, and other relevant evidence.
However, an attack vector is not classified as confirmed simply because it is technically possible. Where the evidence is insufficient, the finding may be reported as NOT DETERMINABLE.
Begin with a confidential case intake and initial assessment.
Do not send highly sensitive evidence through ordinary email unless Greyhawk has specifically instructed you to do so. The appropriate secure evidence-submission method will depend on the case.
COMPLIANCE AND SECURITY
Our operations, platforms, and investigations are aligned with internationally recognized global standards and Philippine regulatory frameworks
Our security management system aligns with ISO 27001 standards for establishing, implementing, maintaining, and continually improving information security.
Digital evidence identification, collection, acquisition, and preservation following internationally recognized forensic guidelines.
Operations structured around NIST CSF core functions: Identify, Protect, Detect, Respond, and Recover for comprehensive security posture.
Full compliance with the Philippine Data Privacy Act, ensuring lawful processing, storage, and protection of personal and sensitive information.
LInvestigations conducted in alignment with the Philippine Cybercrime Prevention Act, ensuring legally admissible digital evidence and procedures.
Rigorous chain-of-custody procedures ensuring digital evidence integrity from acquisition to courtroom presentation, meeting global legal standards.
All data at rest and in transit is encrypted using AES-256 and TLS 1.3 protocols
Comprehensive logging, access controls, and audit trails for full accountability
Strict NDA enforcement and compartmentalized access across all investigations